Build the roles your bank actually has
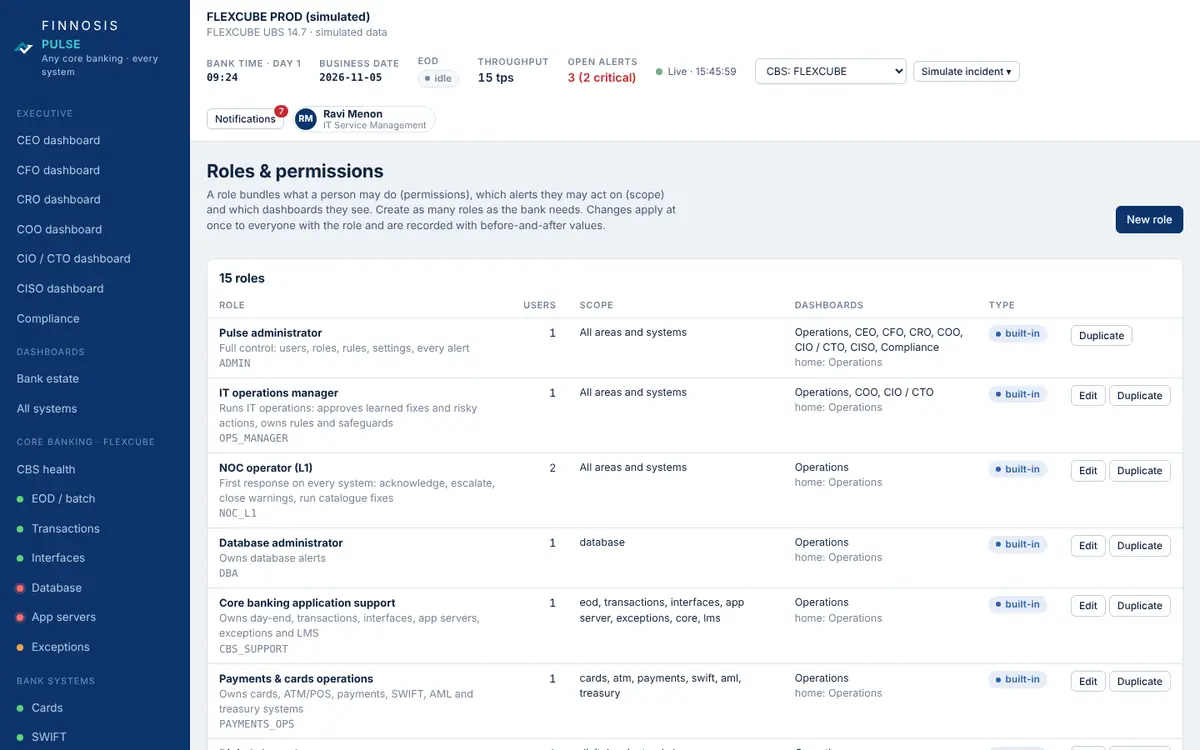
A role combines what a person may do, which systems they may act on, and which dashboards they see. Create as many as you need.
- 15 built-in roles, from NOC operator and DBA to CEO and CISO
- 17 permissions across alerts, remediation, configuration, administration and reports
- Scope by core banking area and by bank system
- Only administrators can grant user or role management
- Nobody can change their own role; the last administrator is protected
Accounts that behave like a bank expects
Hashed, never stored
Passwords are stored as bcrypt hashes on the server.
Five strikes
Five wrong passwords lock the account for 15 minutes; an administrator can unlock it.
Must change at first sign-in
New users and password resets get a temporary password they must replace.
End at once
Disabling a user or resetting a password signs them out everywhere.
Ten reports, ready for the examiner
| Report | What it shows |
|---|---|
| Incident register | Every alert with outcome, root cause, fix, who acknowledged and resolved it, MTTA and MTTR |
| Automatic remediation log | Every fix run with trigger, approver, each step and the verified result |
| Playbook register | Learned fixes with proposer, approver, limits, track record and change history |
| SLA summary | Mean time to acknowledge and resolve by severity and system, automatic vs staff |
| Day-end runs | Run times against the SLA and day-end events |
| User activity | Sign-ins and every action per person |
| Configuration changes | Rules, playbooks, settings, users and roles, before and after |
| Notifications | Every notification with teams and channels |
| Maker-checker | Every playbook and approval-mode fix with maker and checker; self-approval flagged |
| Full audit trail | Every event, append-only; CSV export of any report |
Your data stays in your bank
Runs inside your network
A container in your data centre or private cloud. Monitoring data stays inside the bank.
No writes to bank systems
Read-only database accounts and endpoints; fixes only through your own approved automation.
Your identity provider
AD, LDAP, SAML or OIDC can replace the password step during implementation.
Take Pulse through your security review
We will walk your CISO and audit team through access control, data flows and the audit trail.